Buyer problem
UK organisations sharing personal data with clients, employees, advisers, suppliers and external organisations.
GDPR-conscious sharing is a process, not a badge
No document-sharing tool can make an organisation automatically GDPR compliant. Organisations still need lawful purposes, policies, retention rules, contracts, training and legal judgement. What a platform can do is support safer handling habits for documents that contain personal information.
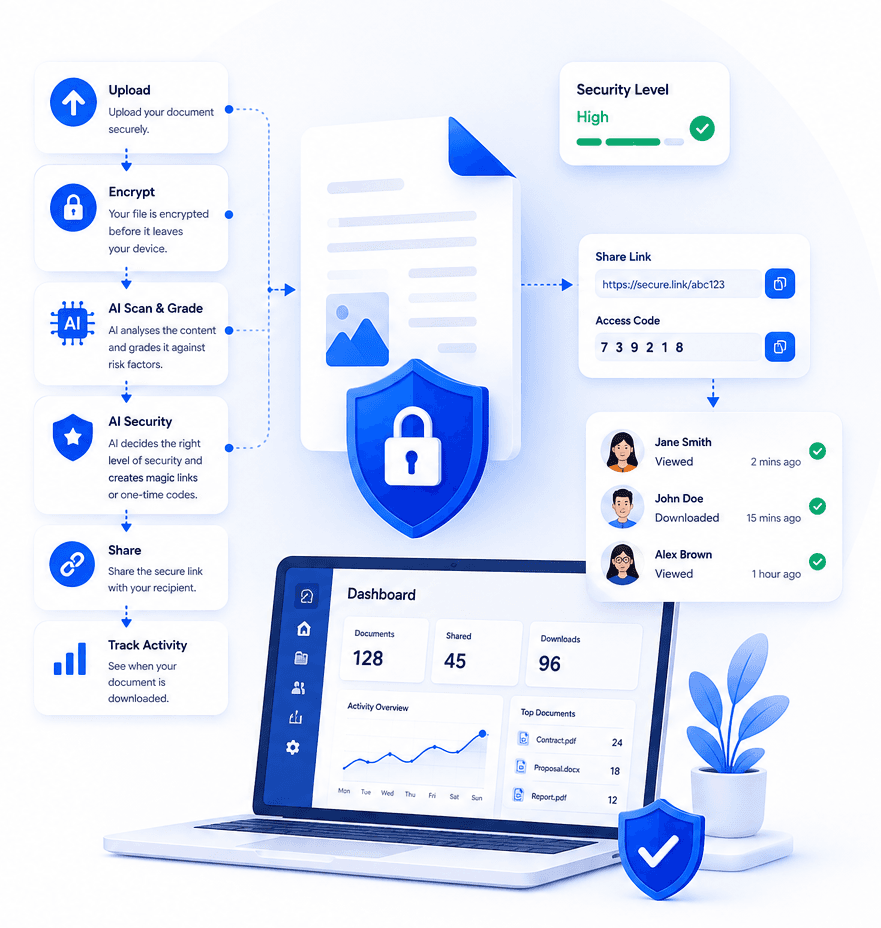
Duckuments is designed to support secure GDPR-conscious document sharing by combining encryption, controlled links, expiry, recipient checks, audit visibility and AI-assisted document risk assessment.
Appropriate security depends on document risk
A routine client letter, a payroll report, an identity document and a medical note should not be handled in exactly the same way. The more sensitive the contents and context, the stronger the sharing controls should be.
AI-supported assessment helps identify personal, financial, employment, legal and confidential content before the file is shared. That gives senders better context for choosing protection such as short expiry, OTP-style verification or tighter download handling.
Reduce unnecessary exposure
Secure sharing starts before the link is sent. Teams should check the recipient, remove unnecessary information, avoid placing personal details in email subject lines and limit how long access remains open.
Duckuments supports this risk-based workflow by keeping the document behind a secure link and recording important activity, rather than distributing uncontrolled attachment copies through inboxes.